
Trailox for Amazon S3
Understand every access path into your S3 data.
See which identities, applications, SDKs and AWS services read your buckets, prefixes and objects. Detect behavioral changes and investigate historical activity. Your data is never read.
What it shows
What Trailox shows in Amazon S3
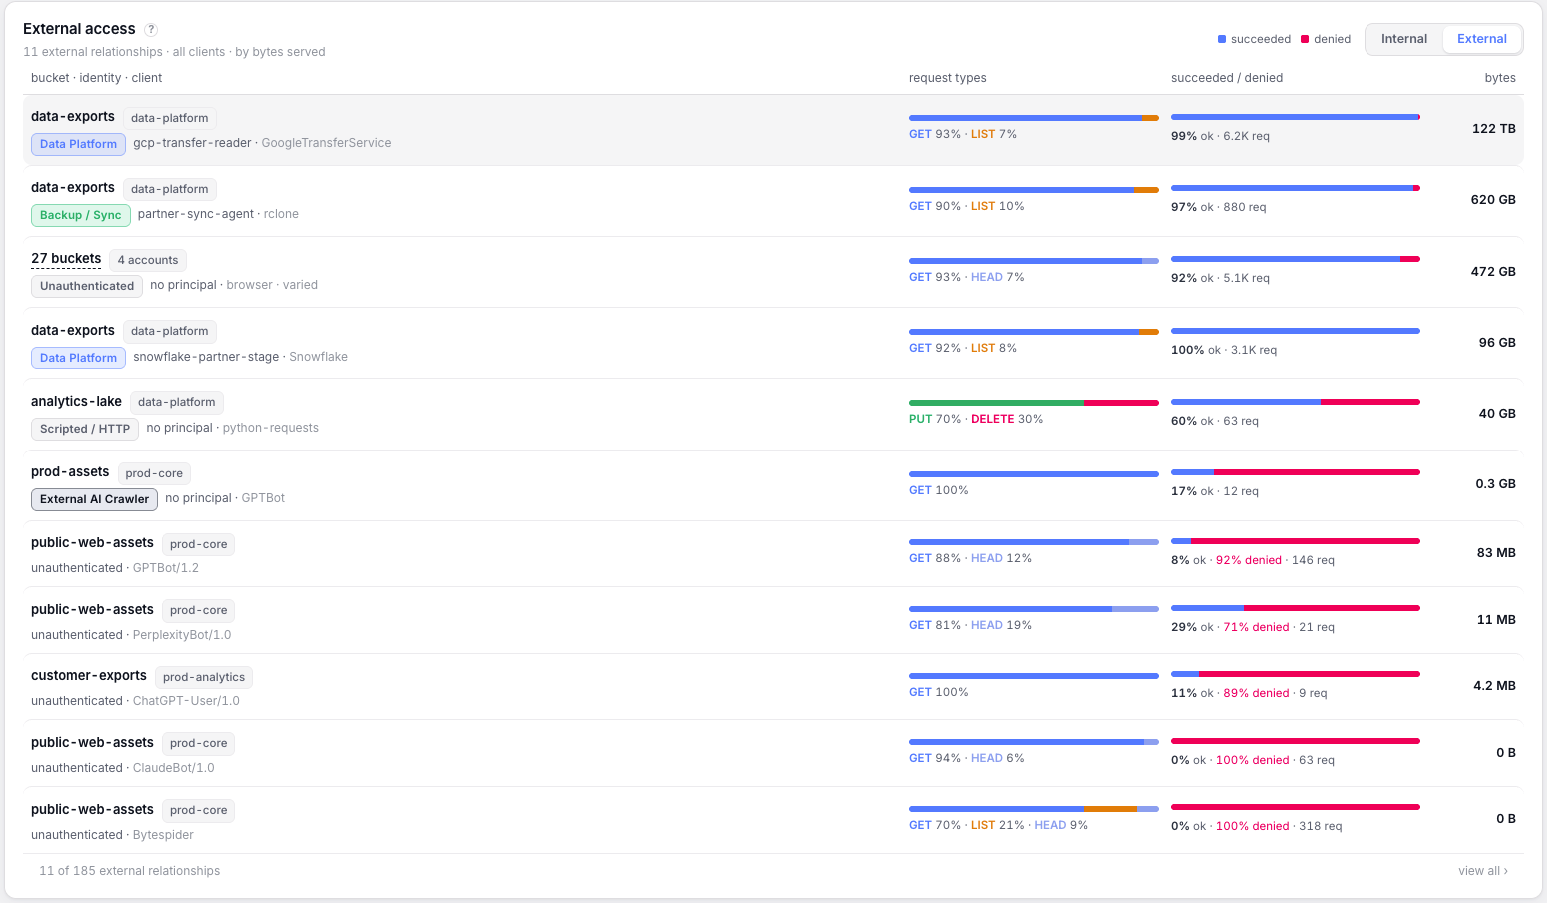
- Access relationships: identities and applications mapped to buckets, prefixes, objects and operations.
- Normal behavior: Trailox learns how each identity reads, and flags reads that do not fit.
- Exports: reads that are anonymous, presigned or from outside your AWS accounts.
- Lakehouse tables: Iceberg, Delta Lake and Hudi tables on S3.
Detections
Behavioral detections for Amazon S3
What it catches
- Stolen keys and logins that still work
- Data copied out of your buckets
- AI agents and service accounts reading outside their task
- Insider misuse by a valid user
Case study, fraud prevention
15,853 successful deletions came from an AWS account outside the primary estate. Every request was allowed.
Read the case studiesFAQ
Questions buyers ask
What does Trailox read in Amazon S3?
Access logs and metadata only. Object contents are never read.
Are Iceberg, Delta Lake and Hudi tables covered?
Yes. Trailox covers Iceberg, Delta Lake and Hudi tables on S3.
Can Trailox see reads from outside my AWS accounts?
Yes. Trailox flags S3 reads that are anonymous, presigned or from outside your AWS accounts.
How do we start?
With a free 14-day Data Access Review. Read-only. First findings in 48 hours.


Start with proof,
not a pitch.
Free 14-day Data Access Review. Read-only. First findings in 48 hours.